
AS Ransomware Analysis Studio — Ransomware Analysis Software
Identify the ransomware, measure how your files were encrypted, and assess what can be recovered — with the evidence for every conclusion.
Overview
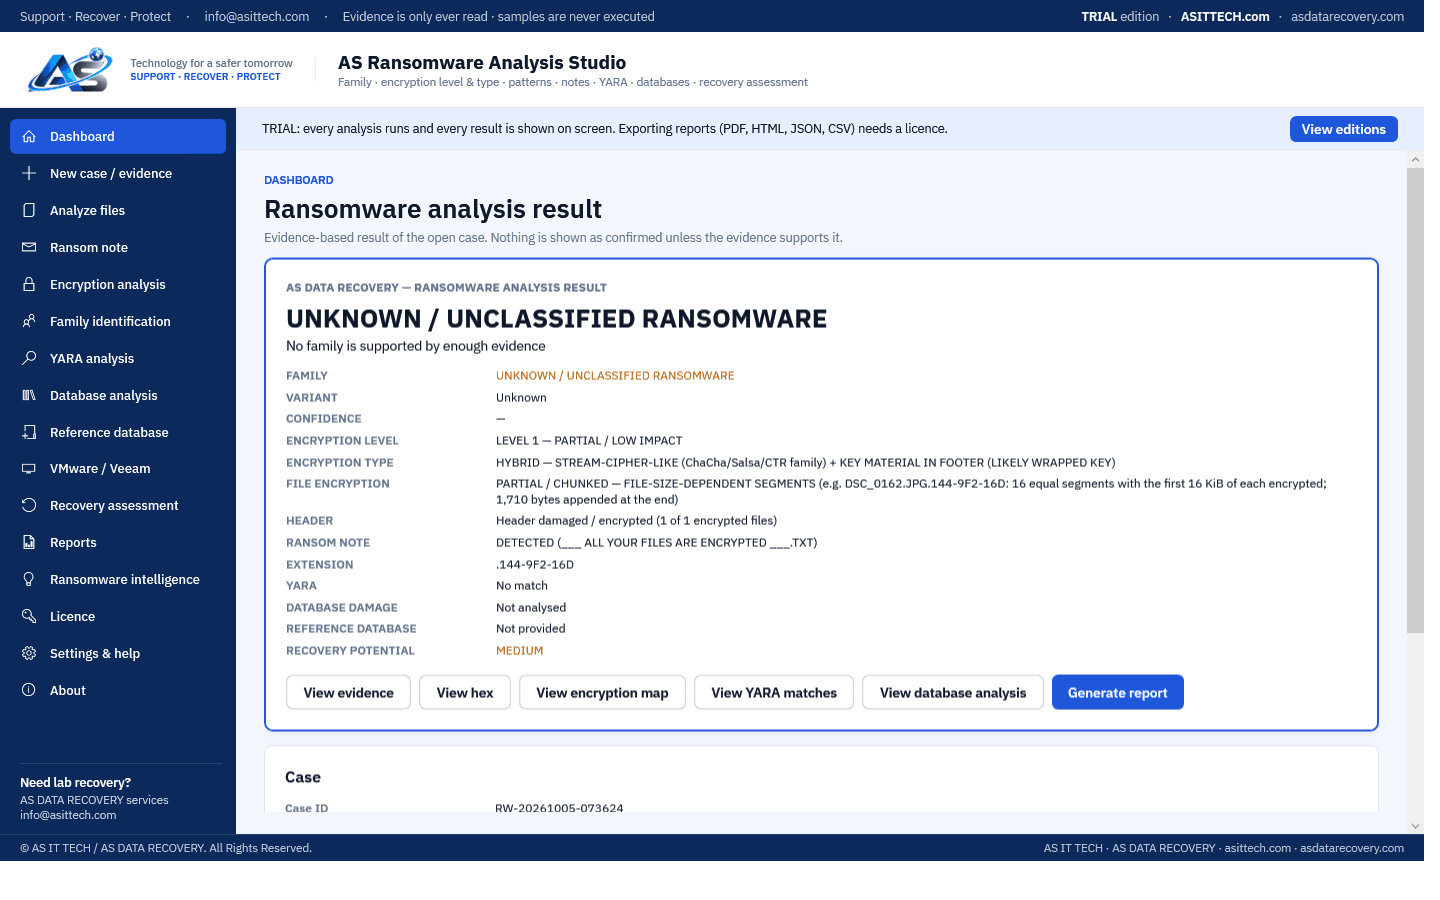
AS Ransomware Analysis Studio is a forensic analysis and recovery-assessment tool for ransomware incidents. It analyses encrypted files, ransom notes, databases, virtual disks, Veeam backups and malware samples (statically — samples are never executed) and reports the likely family with a confidence level and the evidence behind it, never as 100% unless the evidence proves it. It measures how files were encrypted from their structure rather than from entropy alone — the whole file, only the first bytes, chunks at a fixed stride, segments that depend on the file size, the start and end of a database — and the bytes the ransomware appended. With one unencrypted copy of any encrypted file it measures the encryption exactly and tests the cryptography (repeating XOR keys, ECB block ciphers, key blobs in the footer). Everything ends in a recovery assessment and a professional report. Evidence is only ever read.
Physically failed media and complex incidents need a service engagement.
Ransomware recovery servicesSee it work
Features
- Family identification from extension, ransom note, file naming, YARA and encryption behaviour — weighted, with confidence and evidence; UNKNOWN when nothing fits
- Encryption level (0–5), type and pattern: full, head-only, fixed-stride chunks, file-size-dependent segments, database head and tail
- Original vs encrypted comparison: exact encrypted ranges, appended footer, weak-key and block-cipher tests
- Ransom note analysis: victim / decryption IDs, e-mail, Tor, Tox, Telegram, wallets
- YARA engine with built-in and custom rules; static analysis of malware samples
- SQL Server page analysis with reference database comparison; VMware / Hyper-V disks and Veeam backups
- Recovery assessment with legitimate decryptor pointers (No More Ransom) — never a promise of decryption
- Your own intelligence: create family profiles and rules from each case; PDF, HTML, JSON and CSV reports
Supported environments
- Windows 10 / 11, Windows Server (64-bit)
- Encrypted files of any type, ransom notes (TXT, HTML, HTA, RTF), SQL Server MDF / NDF, VMDK / VHD / VHDX, Veeam VBK / VIB
System requirements
- 64-bit Windows
- Copies of the encrypted files and the ransom note(s); an unencrypted copy of any encrypted file improves the measurement
- This is an analysis and assessment tool: it does not decrypt files
Pricing
Choose an edition. Licences are delivered instantly after payment and managed in your customer portal.
Professional
Full recovery features for a single technician or organization.
$1,000
1 activation · One-year licence, including updates during the term. Renewal is 60% of the current price.
Buy nowEnterprise
Everything in Professional, plus higher activation limits, commercial recovery use and priority support.
Price on request
5 activations · One-year licence, including updates during the term. Renewal is 60% of the current price.
Request a quoteFree edition
The free edition runs the full analysis and shows every result on screen. Exporting reports (PDF, HTML, JSON, CSV) requires a licence. Activate it in the program with the licence key from your order.
Download free editionWindows installer, digitally signed by Srinivasan Krishnappa (AS Data Recovery). A new release can show Chrome's “uncommon download” warning until enough people have downloaded it — choose Keep. If Windows SmartScreen appears, click More info → Run anyway.
Documentation and support
User guide, activation instructions and release notes. Licensed customers can open support tickets from the portal.
Frequently asked questions
Does it decrypt my files?
No. It identifies the ransomware, measures the encryption and assesses what can be recovered. Where a legitimate public decryptor exists for the family, it is listed with its compatibility — to be tested on copies first.
How sure is the family identification?
Each kind of evidence (extension, note, file names, YARA, encryption behaviour) has a weight. The result shows the score, the confidence level and every piece of evidence, plus the alternatives. A family is shown as CONFIRMED only with strong evidence from several independent sources; otherwise UNKNOWN / UNCLASSIFIED.
Is the malware executed?
Never. Samples are analysed statically (headers, imports, strings, YARA). Evidence files are only read.
Why is an unencrypted copy of a file useful?
Comparing it with its encrypted version byte by byte shows exactly which parts were encrypted, the footer the ransomware added, and whether the cipher has a weakness — for example a repeating key that decrypts every file.
How do I activate after buying?
Your licence key (ASRA-…) arrives by e-mail and in your account. Open Licence in the program, enter the key under Activate online and click Activate.
Prefer us to recover it for you?
Our lab has already solved 656+ ransomware and data recovery cases. Send us the files instead of running the software yourself: we tell you exactly what we can recover after a free assessment, and if we cannot recover your data, you do not pay.
- ✓ Free assessment before you pay anything
- ✓ No data, no charge
- ✓ NDA on request
Email: info [at] asittech.com · Mon–Fri, 9:00–18:00 IST